Detect the leak, before the breach.
Stealed continuously monitors infostealer logs, combo lists and criminal channels, then alerts you on your own perimeter. Nothing to search, nothing to install.
Free, anonymous search, no account required.
The first calculation for a domain that has never been searched can take a few seconds.
Need help? [email protected]
Confirm you are not a robot to run the analysis.
Infostealer logs, combo lists, forums and criminal Telegram channels, collected and indexed by us.
Its only weapon: a valid credential.
A correct credential, used from a plausible location, triggers nothing. Not the firewall, not the EDR, not the SIEM, not the SOC. Just one log line: authentication succeeded. With a stolen session cookie, even MFA is already behind it.
- [✓] no alertFirewall / NGFWConsistent geolocation, port 443 allowed: nothing to filter.
- [✓] no alertEDR / XDRNo binary, no abnormal action on the endpoint: nothing to detect.
- [✓] no alertSIEMSuccessful authentication on the first attempt: nothing to correlate.
- [✓] no alertSOC 24/7No alert comes up from the stack: nothing to qualify.
- [✓] no alertMFAThe stolen session cookie carries a second factor that was already validated.
of web application attacks involve stolen credentials
Verizon DBIR 2025of ransomware victims had a credential in an infostealer log before the attack
Verizon DBIR 2025between the publication of a stolen credential and a ransomware deployment, often less
Cases observed by Stealed, 2026Three questions, one console.
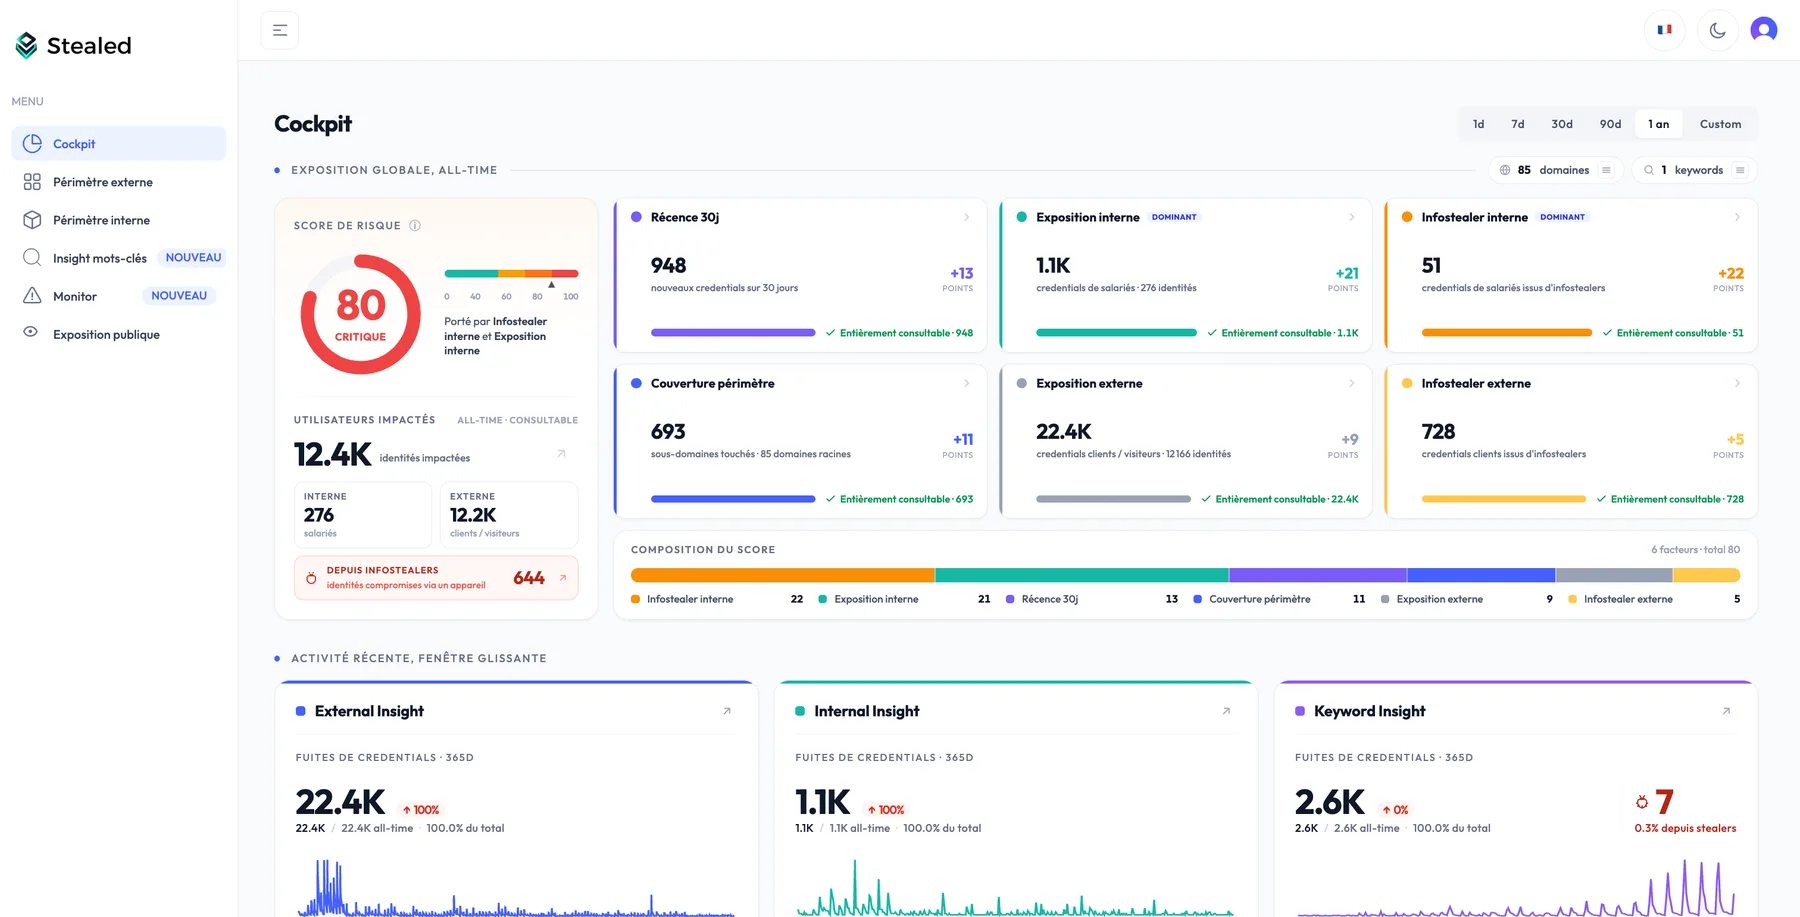
Every leak is correlated with your perimeter from three angles. You receive what concerns you, nothing else.
- Telegram
- forums
- marketplaces
- paste sites
- acme.com
- *.acme.com
- "acme"
Which employee is already compromised?
Credentials whose e-mail address is on your domains, and the sites where they leaked.
- login
- j.doe@acme.com
- url
- https://sharepoint.example.com/login
- source
- infostealer · lumma
Which user of my services signs in with a stolen access?
Credentials whose login URL points at your services: customers, partners, contractors.
- login
- [email protected]
- url
- https://vpn.acme.com/sslvpn
- source
- combolist · ulp
Which contractor, project or brand shows up in a leak?
Your keywords spotted in leak URLs, even when your domain is not there.
- login
- [email protected]
- url
- https://acme.example.com/portal
- source
- infostealer · redline
From raw leak to qualified alert.
Two kinds of leak in, one format out, and an alert only when it concerns you.
Own collection
Telegram, forums, marketplaces, paste sites. No broker, no purchased data.
Normalisation and deduplication
A credential seen fifteen times is one leak, not fifteen alerts.
Correlation with your perimeter
DNS-verified domains, validated keywords. Nothing beyond.
Alert where you work
E-mail, Slack, Teams, signed webhook, SIEM.
- 500M+
- credentials per day
- 14B+
- unique credentials indexed
- < 60 min
- from publication to availability
- < 5 min
- to open a workspace
Built for the people who have to act.
From the CISO of a regulated mid-market company to the MSSP operating a hundred clients.
SMBs and startups
Enterprise-grade protection, without a dedicated security team.
- › Ready in five minutes, nothing to install
- › Only the alerts that matter
- › From 1,500 EUR excl. VAT per year
Mid-market and regulated sectors
NIS2 and DORA expect continuous monitoring of your exposure. Here it is, operational within the hour.
- › Multi-domain perimeter verified by DNS
- › Exportable audit log for the regulator
- › Alerts straight into your SOC or SIEM
Large enterprises
An extended perimeter, isolated access, native integration.
- › REST API and SIEM / SOAR integration
- › SLA and dedicated support
- › Early access to new modules
MSSPs and managed service providers
Your whole client portfolio, one console.
- › Exposure score per client
- › Import your client base in seconds
- › White-label reports
What security teams are saying
The API was integrated into our stack in less than a day. We now offer credential monitoring to our clients as an add-on service.
Clean interface, setup in 30 minutes. We monitor our domains without needing a dedicated security team.
We monitor 12 subsidiaries from a single dashboard. Subdomain granularity lets us pinpoint exactly which entity is exposed.
The data is fresh and actionable. We detected compromised client credentials before they even knew about it.
Integrated with our SIEM in a few hours. Webhooks allow us to automate incident response directly.
We monitor emails of our lawyers and sensitive clients. The tool is simple, alerts are precise.
The API was integrated into our stack in less than a day. We now offer credential monitoring to our clients as an add-on service.
Clean interface, setup in 30 minutes. We monitor our domains without needing a dedicated security team.
We monitor 12 subsidiaries from a single dashboard. Subdomain granularity lets us pinpoint exactly which entity is exposed.
The data is fresh and actionable. We detected compromised client credentials before they even knew about it.
Integrated with our SIEM in a few hours. Webhooks allow us to automate incident response directly.
We monitor emails of our lawyers and sensitive clients. The tool is simple, alerts are precise.
A demo on your perimeter, not on a demo dataset.
Console tour, API integration, leaks detected on your domains, live.
- [✓] No commitment
- [✓] No installation